Skip to content
Search

Latest Stories

Submit Guest Post

Horizon scandal victims to get payouts for data leak

 Post Office Horizon

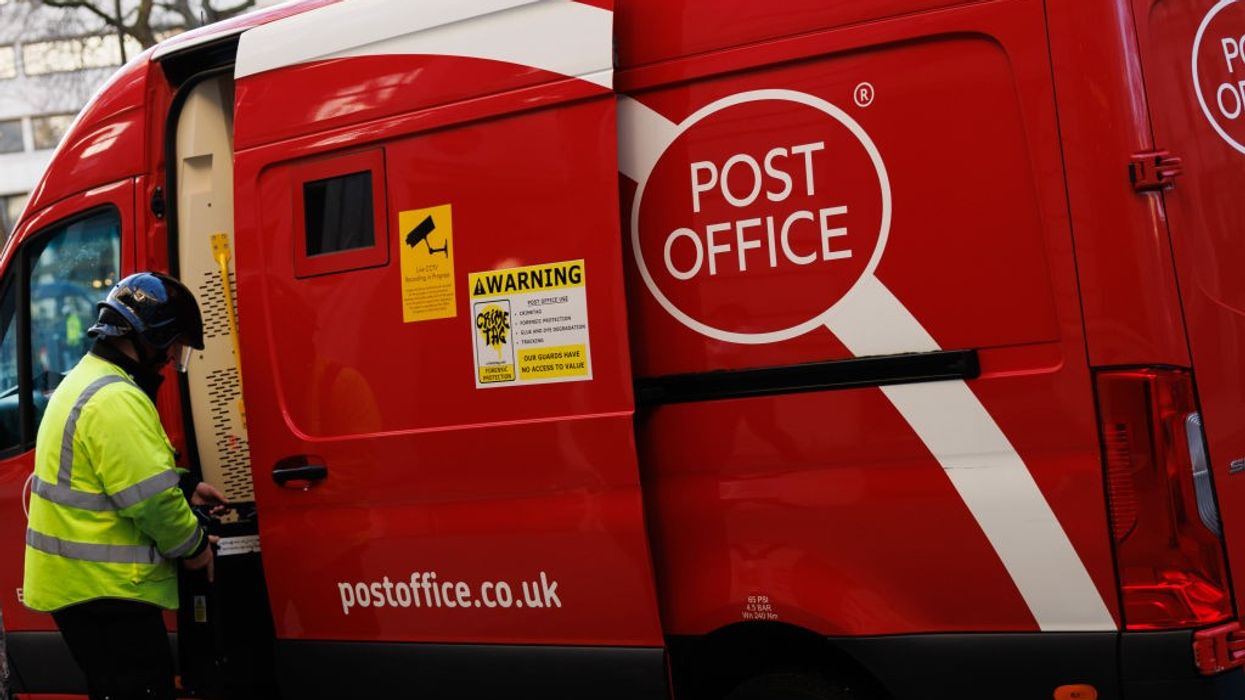
A Post Office van parked outside the venue for the Post Office Horizon IT inquiry at Aldwych House on January 11, 2024 in London. (Photo: Getty Images)

Getty Images

THE POST OFFICE has agreed to compensate hundreds of former sub-postmasters after their personal data was accidentally published on its corporate website.

The breach, revealed in June 2023, exposed the names and addresses of 555 people who were part of the Horizon IT scandal.


According to the BBC, affected individuals will receive either £5,000 or £3,500, depending on whether they were living at the published address at the time. Higher payouts may be available for those who choose to pursue further claims.

The Post Office has apologised for the breach and said it is working in “full co-operation” with the Information Commissioner’s Office. Former chief executive Nick Read had previously described the leak as a “truly terrible error.”

Law firm Freeths, which represented 555 sub-postmasters in a 2017 High Court case, confirmed it secured the payouts. Of the 420 clients Freeths represents in a separate compensation process, 348 have already received payments.

Chris Head, a former sub-postmaster, said the mistake took “far too long to right” and described its emotional toll. Freeths partner Will Richmond-Coggan told BBC the agreement required no formal claims and allows further action.

The Post Office urged affected individuals to get in touch directly or through their solicitors.
Add EasternEye As Your Trusted Source
preferred source on google news

More For You

php vulnerability 2026

Cybersecurity agencies have urged website operators to prepare for urgent software updates following warnings over critical vulnerabilities

iStock [Representational image]

Millions of websites face a security scare. Here's what you need to know

  • Two critical vulnerabilities in PHP, software used by many websites, have been rated 9.2 out of 10 under a cybersecurity severity scale.
  • Cloudflare says it has seen early attacks, while European cybersecurity officials warn that the flaws could allow hackers to take control of vulnerable servers.
  • Website owners and hosting providers are being urged to apply patches immediately, while ordinary users should remain alert to suspicious activity.

Millions of websites could face a security risk after developers of widely used website software announced plans to release emergency fixes for two critical vulnerabilities.

The software, called PHP, helps websites display content and run features such as online shopping, account logins and other interactive services. It is used by platforms including WordPress, Drupal, Joomla and Magento, meaning the flaws could affect a broad range of websites.

Keep ReadingShow less